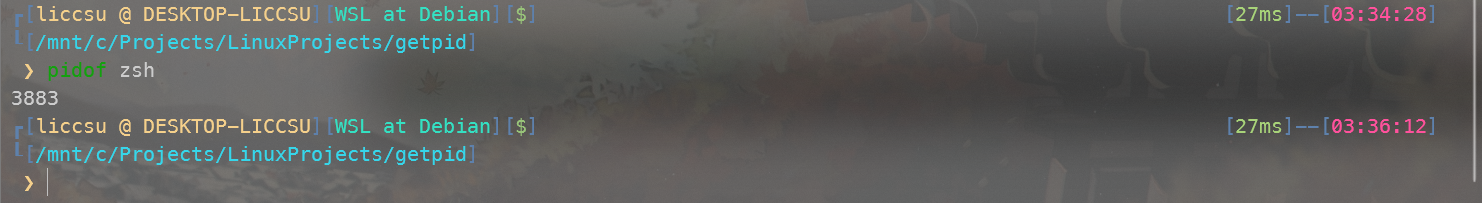
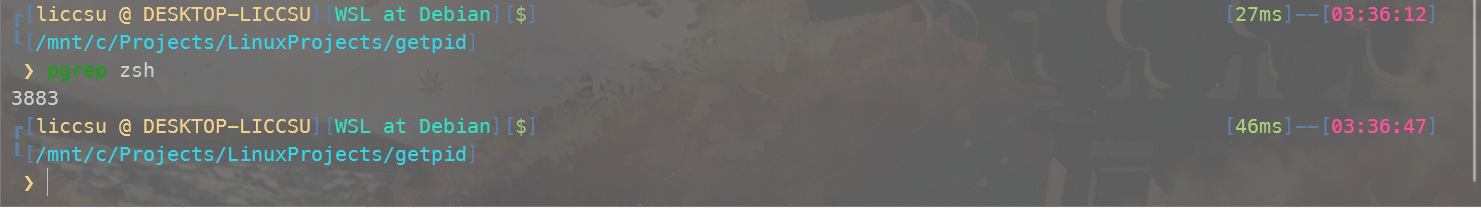
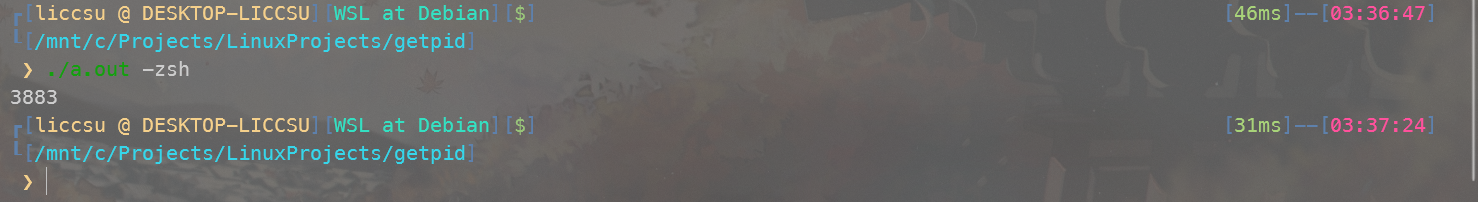
pid_tget_pid_t(constchar *cmd) { DIR *dir; FILE *file; structdirent *ent; char filename[256], cmdline[256]; pid_t pid = -1; dir = opendir("/proc");
if (dir != NULL) { while ((ent = readdir(dir))) { if (ent->d_type == DT_DIR && STR_IS_INT(ent->d_name)) { snprintf(filename, sizeof(filename), "/proc/%s/cmdline", ent->d_name); file = fopen(filename, "r"); if (file) { fgets(cmdline, sizeof(cmdline), file); fclose(file); if (strcmp(cmd, cmdline) == 0) { pid = atoi(ent->d_name); break; } } } } closedir(dir); }
return pid; }
三、通过进程号获取struct pid
先看一下struct pid的定义:
1
2
3
4
5
6
7
8
9
10
11
structpid { atomic_t count; // pid的引用计数 unsignedint level; // pid的层级 /* lists of tasks that use this pid */ structhlist_headtasks[PIDTYPE_MAX]; /* wait queue for pidfd notifications */ wait_queue_head_t wait_pidfd; structrcu_headrcu;// RCU头, 用于RCU同步机制 structupidnumbers[1];// 用于储存pid号的结构体数组 };
其中struct upid定义如下:
1
2
3
4
5
6
7
structupid { /* Try to keep pid_chain in the same cacheline as nr for find_vpid */ int nr; /* the pid value */ structpid_namespace *ns;/* namespace */ structhlist_nodepid_chain;/* hash chain */ };
structcred { atomic_t usage; #ifdef CONFIG_DEBUG_CREDENTIALS atomic_t subscribers; /* number of processes subscribed */ void *put_addr; unsigned magic; #define CRED_MAGIC 0x43736564 #define CRED_MAGIC_DEAD 0x44656144 #endif kuid_t uid; /* real UID of the task */ kgid_t gid; /* real GID of the task */ kuid_t suid; /* saved UID of the task */ kgid_t sgid; /* saved GID of the task */ kuid_t euid; /* effective UID of the task */ kgid_t egid; /* effective GID of the task */ kuid_t fsuid; /* UID for VFS ops */ kgid_t fsgid; /* GID for VFS ops */ unsigned securebits; /* SUID-less security management */ kernel_cap_t cap_inheritable; /* caps our children can inherit */ kernel_cap_t cap_permitted; /* caps we're permitted */ kernel_cap_t cap_effective; /* caps we can actually use */ kernel_cap_t cap_bset; /* capability bounding set */ kernel_cap_t cap_ambient; /* Ambient capability set */ #ifdef CONFIG_KEYS unsignedchar jit_keyring; /* default keyring to attach requested * keys to */ structkey __rcu *session_keyring;/* keyring inherited over fork */ structkey *process_keyring;/* keyring private to this process */ structkey *thread_keyring;/* keyring private to this thread */ structkey *request_key_auth;/* assumed request_key authority */ #endif #ifdef CONFIG_SECURITY void *security; /* subjective LSM security */ #endif structuser_struct *user;/* real user ID subscription */ structuser_namespace *user_ns;/* user_ns the caps and keyrings are relative to. */ structgroup_info *group_info;/* supplementary groups for euid/fsgid */ /* RCU deletion */ union { int non_rcu; /* Can we skip RCU deletion? */ structrcu_headrcu;/* RCU deletion hook */ }; };
五、更改权限
将得到的struct cred中的以下几个成员变量赋值0:
1
2
3
4
5
6
7
8
kuid_t		uid;		/* real UID of the task */
kgid_t		gid;		/* real GID of the task */
kuid_t		suid;		/* saved UID of the task */
kgid_t		sgid;		/* saved GID of the task */
kuid_t		euid;		/* effective UID of the task */
kgid_t		egid;		/* effective GID of the task */
kuid_t		fsuid;		/* UID for VFS ops */
kgid_t		fsgid;		/* GID for VFS ops */